Burger King Russia Data Breach Exposes 3.2M Customer Records via Mindbox
Burger King Russia suffered a data breach in 2024 after attackers targeted its marketing automation platform, Mindbox. The incident exposed 3.2 million customer records, including personal information like emails, phone numbers, and geolocations. While payment details were not compromised, the breach highlights the risks of supply-chain attacks and third-party vendor vulnerabilities.
LazyFounders
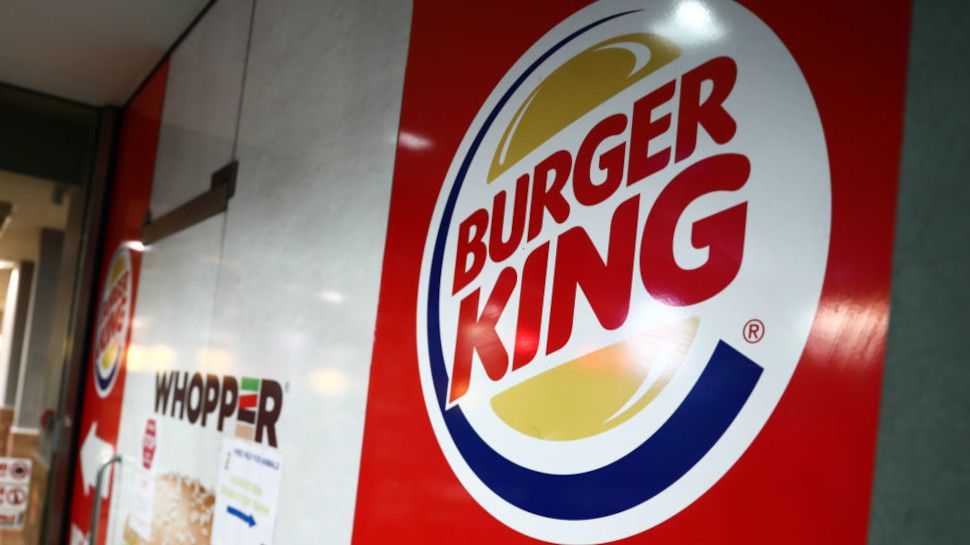
Burger King Russia suffered a data breach in 2024 after attackers targeted its marketing automation platform, Mindbox. The incident exposed 3.2 million customer records, including personal information like emails, phone numbers, and geolocations. While payment details were not compromised, the breach highlights the risks of supply-chain attacks and third-party vendor vulnerabilities.
30 SEC SUMMARY
- Burger King Russia experienced a data breach in 2024 via its marketing automation platform, Mindbox, exposing 3.2 million customer records.
- The leaked data includes emails, names, genders, birth dates, phone numbers, and geolocations from 2018 to 2024, but no payment details.
- Mindbox reported this as its first serious security incident and claimed the breach was quickly contained.
- The attack was likely identity-based, prompting Mindbox to enforce stricter access controls and mandatory two-factor authentication.
- Over 1,100 businesses, including L’Oréal and KFC, use Mindbox for personalized marketing campaigns.
TABLE OF CONTENTS
- What Happened
- Mindbox’s Response
- Nature of the Attack
- What this means
- Key takeaways
- FAQ
- Sources
KEY HIGHLIGHTS
- Burger King Russia’s 2024 data breach exposed 3.2 million customer records via its marketing automation platform, Mindbox.
- Leaked data included emails, names, genders, birth dates, phone numbers, and geolocations spanning 2018 to 2024.
- Mindbox reported this as its first serious security incident and contained it quickly using threat detection tools.
- The attack was likely identity-based, prompting Mindbox to implement stricter access controls and mandatory two-factor authentication.
- Payment details were not compromised, but the breach poses risks for phishing and identity theft.
What Happened
According to TechRadar, Burger King Russia experienced a data breach in 2024 through its marketing automation platform, Mindbox. The incident exposed 3.2 million customer records, including emails, names, genders, birth dates, phone numbers, and geolocations collected between 2018 and 2024. Payment details were not compromised, according to the reports.
Mindbox, a Moscow-based marketing automation provider, powers personalized, omnichannel campaigns for over 1,100 businesses, including L’Oréal, Panasonic, KFC, JBL, and United Colors of Benetton. The platform collects and processes customer data to enable targeted marketing efforts.
Mindbox’s Response
Mindbox stated that this was its first serious information security incident, as reported by TechRadar. The company claimed the breach was detected and contained quickly using its threat detection tools.
Following the incident, Mindbox reformed its internal role system to enforce stricter, more granular permissions. The platform also introduced mandatory two-factor authentication (2FA) and limited project access scenarios. Additionally, it implemented a mechanism requiring employee confirmation for access requests.
Nature of the Attack
Initial reports suggested that around 5.6 million lines of data were exposed, though the confirmed number stands at 3.2 million records. According to TechRadar, the breach was likely the result of an identity-based attack, rather than a zero-day exploit. This type of attack typically involves compromised credentials or social engineering rather than a technical vulnerability.
Burger King Russia has reportedly assured customers that no payment or passport details were leaked. However, the exposed data—such as emails and phone numbers—can still be exploited for phishing campaigns or identity theft.
What this means
LazyFounders analysis — our interpretation, not reported fact.
For founders and operators, this breach is a reminder of the risks tied to third-party vendors, especially in marketing automation. Even if a platform has a strong track record, like Mindbox, no system is immune to identity-based attacks. The incident underscores the importance of vetting vendors for security practices, enforcing strict access controls, and mandating multi-factor authentication (MFA) for all internal and external systems.
For startups handling customer data, this is also a lesson in transparency. Burger King Russia’s quick communication about what wasn’t leaked (payment details) may help mitigate reputational damage. However, the long-term impact of exposing personal data—such as emails and phone numbers—can’t be ignored, as it fuels phishing and identity theft risks for affected customers.
The takeaway? Assume breaches will happen. Build redundancies, monitor third-party access, and have a crisis plan ready.
Key takeaways
- Burger King Russia’s data breach exposed 3.2 million customer records via its marketing platform, Mindbox.
- Leaked data includes personal information like emails, names, and phone numbers, but no payment details.
- Mindbox called this its first serious security incident and implemented stricter access controls post-breach.
- Identity-based attacks, rather than zero-day exploits, are a growing threat to businesses.
- Founders should audit third-party vendors for security risks and enforce MFA to reduce attack surfaces.
FAQ
What data was leaked in the Burger King Russia breach?
The breach exposed 3.2 million customer records, including emails, names, genders, birth dates, phone numbers, and geolocations collected between 2018 and 2024. Payment details were not compromised.
How did Mindbox respond to the breach?
Mindbox stated this was its first serious security incident. It quickly contained the breach using threat detection tools and implemented stricter access controls, mandatory two-factor authentication, and a mechanism for employee confirmation of access requests.
What type of attack caused the Burger King Russia breach?
The attack was likely identity-based, involving compromised credentials or social engineering, rather than a zero-day exploit or technical vulnerability.
Which companies use Mindbox?
Mindbox is used by over 1,100 businesses, including L’Oréal, Panasonic, KFC, JBL, and United Colors of Benetton, for personalized marketing campaigns.
Related on LazyFounders
Sources
- TechRadar · 2026-09-23
Millions of Russian fast food fans hit in Burger King Russia hack
This story is an original summary and analysis written by LazyFounders from the reporting listed above. Facts are attributed to their original publishers; sections marked as analysis are LazyFounders's opinion. Where a source is in another language, facts were machine-translated and quotations are reported, not reproduced. Read the original coverage via the links.